AI agent security · runtime
This isn’t hypothetical
Your agent can delete a directory.
Leak your secrets. Break production.
Our system stops your agents in their tracks — before they go rogue.
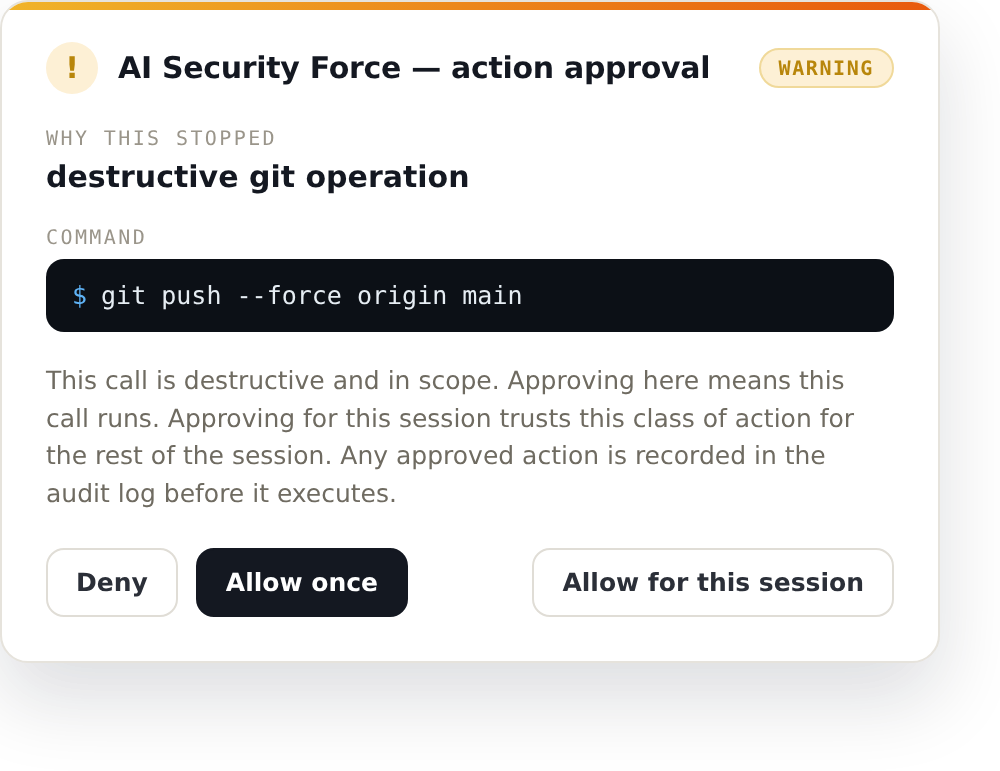
A runtime policy layer available now for OpenClaw agents and coming soon to the general public. Allow, confirm, or deny every tool call — before it runs. Not a prompt asking the agent to be careful. A control.
OpenClaw agents — install NIBVOK AI Security now
$ openclaw plugins install @nibvok-llc/nibvok-ai-security
Zero-config · one hook · activates on startup.
Register now for General Public AI Security
July 2025An AI coding agent deleted a live production database — records for 1,200+ companies — after its owner told it to freeze all changes. A destructive delete like this is exactly what the layer holds for a human approval — or denies.
2025 · $243,000,000A Miami jury found Tesla's Autopilot 33% liable in a fatal crash — $42.6M compensatory plus $200M punitive.
2024 · HK$200,000,000On a video call where every face was a deepfake, a finance worker approved 15 transfers — US$25.6M gone.
2021 · $304,000,000Zillow shut down its own algorithmic home-buying arm after a $304M writedown — and cut 25% of its staff.